
Table of contents
Identity and access management is the control that almost every IT leader agrees is the highest-leverage security work available to them — and the one that quietly slides to next quarter, every quarter. It is not glamorous. It does not demo well. It rarely arrives as an urgent ticket. Yet when an incident does land, the post-mortem usually traces back to a stale admin account, a shared credential, or a multi-factor prompt that a tired user approved at 11pm. Getting identity and access management right is the difference between an attacker being locked out at the front door and an attacker wandering the building with a valid badge.
Why identity and access management keeps slipping down the list
The honest answer is that identity and access management is never finished. A firewall migration has an end date. A backup platform has a go-live. Identity work, by contrast, is a permanent operating discipline: every new starter, every leaver, every contractor, every acquired company and every SaaS tool your client signs up for changes the shape of the problem. Managed service providers running lean teams will always prioritise the thing with a deadline over the thing without one.
There is a second, less comfortable reason. Identity and access management touches people. Tightening conditional access means someone senior will be prompted more often. Removing standing administrative rights means a developer loses a shortcut they have used for three years. Reviewing access quarterly means asking department heads to actually read a list and make decisions. Technical controls are easy compared with the negotiation, and negotiation takes hours that no one has budgeted.
The third reason is skills. Doing identity and access management properly requires someone who understands conditional access policy design, directory hygiene, privileged access models and the specific failure modes of token theft — and who has the time to sit with those problems weekly rather than in a two-day sprint once a year. That combination of specialist knowledge and sustained availability is exactly what most MSPs and mid-sized IT teams cannot recruit affordably in the UK or EU.
What strong identity and access management looks like in 2026
The direction of travel is clear and well documented. National guidance has converged on a few principles: prefer phishing-resistant authentication, assume credentials will be stolen, and design so that a stolen credential alone is not enough. The UK’s National Cyber Security Centre sets out practical expectations in its guidance on multi-factor authentication for corporate online services, while NIST Special Publication 800-63B provides the underlying authenticator assurance model that most frameworks borrow from.
Translated into day-to-day terms, mature identity and access management in 2026 means a handful of things holding true at once. Every human account authenticates with a method that cannot be relayed by a proxy phishing kit. Administrative privilege is requested and granted for a window, not held permanently. Joiners, movers and leavers are processed through a defined workflow rather than an email to the service desk. Service accounts and API tokens have owners, expiry dates and a place they are recorded. And someone reviews the exceptions — because there are always exceptions — on a schedule that does not depend on anyone remembering.
Notice that none of this is a product purchase. Most organisations already own the licences they need; Microsoft Entra ID P1 or Business Premium covers the majority of what a small or mid-sized client requires. The gap is almost never the tooling. The gap is the sustained specialist attention needed to configure it, roll it out without a revolt, and keep it true as the environment drifts.
7 proven identity and access management wins
If you can only fund a limited amount of identity and access management work this quarter, these are the moves that return the most risk reduction per hour spent. They are ordered roughly by ratio of impact to effort.
1. Move privileged accounts to phishing-resistant authentication first
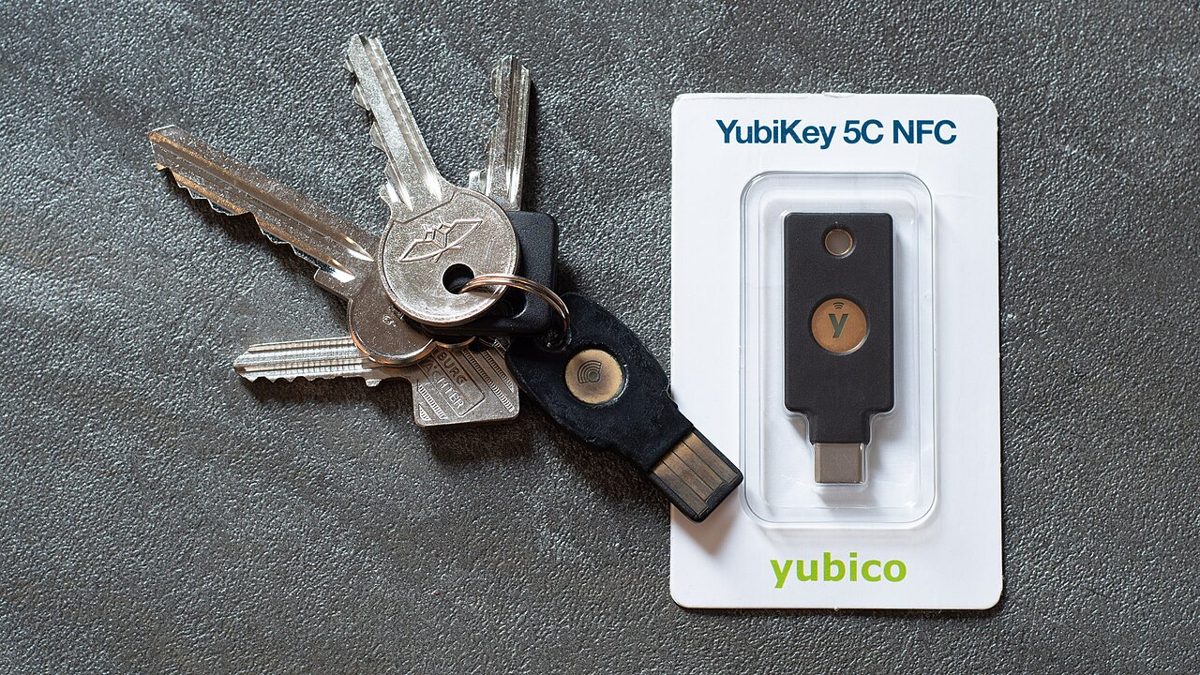
Do not attempt a full-population rollout as your opening move. Identify every account with administrative rights — including the break-glass accounts, the partner-tenant accounts your own engineers use, and the third-party consultant logins — and move that population to FIDO2 keys or passkeys. It is a small, well-defined group, it removes the highest-value target from the phishing board, and it gives you a working pattern to reuse.
2. Eliminate standing administrative privilege
Permanent global administrator rights are the single most consequential identity and access management flaw in most tenants. Just-in-time elevation, where an engineer requests a role for a bounded window with a reason recorded, converts a permanent liability into an auditable event. It also produces something genuinely useful for client reporting: a record of who did privileged work, when, and why.
3. Fix the leaver process before anything else in the joiner-mover-leaver chain
Orphaned accounts are the cheapest possible entry point for an attacker and the easiest gap to close. A defined offboarding workflow that disables sign-in, revokes active sessions and tokens, and reassigns data ownership within an agreed window is basic identity and access management hygiene — and it is astonishing how many otherwise well-run environments have no such workflow written down.
4. Design conditional access as a small set of readable policies
Conditional access estates decay into dozens of overlapping rules that nobody dares change. Aim instead for a compact, documented policy set where each rule has a stated purpose. Fewer, clearer policies are easier to test, easier to hand to another engineer, and far less likely to produce the exception that quietly disables protection for a whole group.
5. Give every service account an owner and an expiry
Non-human identities now outnumber human ones in most estates, and they are frequently the weakest part of an identity and access management programme: created for a project, granted broad rights for convenience, and never reviewed. A simple register — what it is, who owns it, what it may access, when it expires — is unglamorous work that repeatedly turns out to matter.
6. Run access reviews that produce decisions, not spreadsheets
An access review that ends with a department head clicking “approve all” is theatre. Reviews work when the list is short, scoped to one team, framed as specific questions, and when someone chases the non-responses. That chasing is genuine recurring labour, and it is the most common reason identity and access management reviews lapse after two cycles.
7. Monitor for identity-based attack patterns, not just failed logins
Impossible-travel alerts and brute-force counters are table stakes. The patterns worth investing in are the ones that indicate token theft and session hijacking: an unfamiliar sign-in that skips authentication entirely, new mail forwarding or inbox rules appearing shortly after a sign-in, or a device registration you cannot account for. These require someone competent watching during working hours — which brings us to the real constraint.
The staffing gap behind every identity and access management programme
Every item on that list is well understood. None of it is secret knowledge. The reason identity and access management programmes stall is almost never that the team does not know what to do — it is that the work is continuous, moderately specialised, and competing with a ticket queue that generates visible pressure every hour of the day.
This is a resourcing problem wearing a technology costume. A UK or EU security engineer with real conditional access and privileged access experience is expensive and scarce, and hiring one full-time is difficult to justify for a workload that is genuinely part-time per client but adds up across a portfolio. So the work gets squeezed into the gaps, and the gaps close.
The organisations that succeed at identity and access management tend to solve it structurally rather than heroically. They give the work a named owner with protected hours, they define what “done” looks like for each client, and they stop expecting the same engineers who are firefighting the service desk to also drive a long-horizon security programme. The question then becomes how to fund that named owner without wrecking the margin.
How OutsourceZA closes the identity and access management gap
This is precisely the shape of problem that outstaffing solves well. OutsourceZA places skilled South African security and infrastructure engineers into UK and European MSPs and IT teams as dedicated members of your team — not a ticket-based helpdesk contract, but named people who learn your clients, your tooling and your standards.
Three things make it work for identity and access management specifically. First, cost: South African engineering talent typically delivers a 40–60% saving against equivalent UK or EU salaries, which turns a hard-to-justify part-time role into an easy one. Second, timezone: South Africa sits within an hour or two of UK and Central European time for most of the year, so your identity engineer is online for the same change windows, the same stand-ups and the same client calls — genuine overlap rather than an overnight handover. Third, capability: South Africa has a deep pool of engineers trained in Microsoft, cloud and security stacks, working in English, in an environment where MSP-style multi-tenant work is well understood.
Outstaffing also gives you flexibility that direct hiring does not. You can start with one engineer at a fraction of a full-time equivalent to get an identity and access management baseline in place across your client estate, then scale up as the programme grows or as you win security-led business. You can find more detail on how the model works on our IT outsourcing services page, and read about the team and how we vet engineers on our about us page.
A practical 90-day rollout plan
If you want a starting point you can actually run, this is a realistic sequence for bringing identity and access management under control across a client base without disrupting delivery.
Days 1–30: establish the truth. Inventory every privileged account, every service account and every conditional access policy across your tenants. Do not change anything yet. The output is a written baseline per client and a shortlist of the three most dangerous findings — usually a permanently privileged account, an unowned service identity, and a conditional access exception nobody remembers creating.
Days 31–60: harden the top of the pyramid. Move all administrative accounts to phishing-resistant authentication, establish break-glass accounts with documented procedures, and implement just-in-time elevation for the roles that support it. Rationalise conditional access into a documented policy set. This phase delivers the majority of the risk reduction.
Days 61–90: make it repeatable. Write and test the joiner-mover-leaver workflow, stand up the service account register with owners and expiry dates, schedule the first access review cycle, and agree what gets reported to each client monthly. The goal of this phase is that identity and access management continues without depending on the person who started it.
Ninety days is achievable with roughly one dedicated engineer across a small portfolio. It is not achievable as a side-of-desk task, which is the entire point.
Identity and access management FAQ
Is multi-factor authentication enough on its own?
No. MFA remains essential and blocks a large share of commodity credential attacks, but not all MFA is equal. Push notifications and one-time codes can be relayed by modern phishing kits or worn down by prompt fatigue. Phishing-resistant methods such as FIDO2 keys and passkeys are bound to the device and the site, which is why guidance from bodies such as the NCSC and NIST points firmly in that direction.
We are a small MSP. Do we need a dedicated identity engineer?
Not necessarily a full-time one — but you do need protected, recurring hours with a named owner. The failure pattern is treating identity work as something everyone does a bit of, which means nobody does it consistently. A part-time dedicated resource, whether internal or outstaffed, is far more effective than four engineers each spending an occasional hour.
How does outstaffing differ from outsourcing our security to a third party?
Outsourcing hands a function to an external provider who runs it their way. Outstaffing gives you additional engineers who work inside your processes, on your tooling, under your management, as part of your team. For identity and access management that distinction matters, because the work depends on knowing your clients’ environments and politics in detail. If you would like to talk it through, get in touch.
How long before we see measurable improvement?
Meaningful risk reduction typically arrives in the first 60 days, because hardening privileged accounts is fast and high-impact. The operational discipline — reviews, joiner-mover-leaver, service account governance — takes a full quarter to embed and then becomes routine. Engineers interested in this kind of work can see current openings on our IT jobs page.
Where should we start if our environment is a mess?
Start with an inventory, not a change. You cannot secure what you have not enumerated, and the inventory itself usually surfaces two or three findings worth fixing that week. From there, work top-down: privileged accounts first, then the leaver process, then everything else. A disciplined identity and access management programme is built out of small, ordered steps rather than a single transformation project.
Identity and access management rewards consistency more than brilliance. The organisations that get it right are rarely the ones with the largest budgets — they are the ones that gave the work a named owner, protected the hours, and kept going after the initial push. If the constraint holding you back is capacity rather than knowledge, that is a solvable problem, and it is the one we solve every day.
Book your consultation
Book a chat with Niel or Johan so we can understand exactly what (and who) you need for your business to succeed. It’s also a great time to ask any questions you may have. See you soon!